
AI in government: CIOs, take the lead before it’s too late


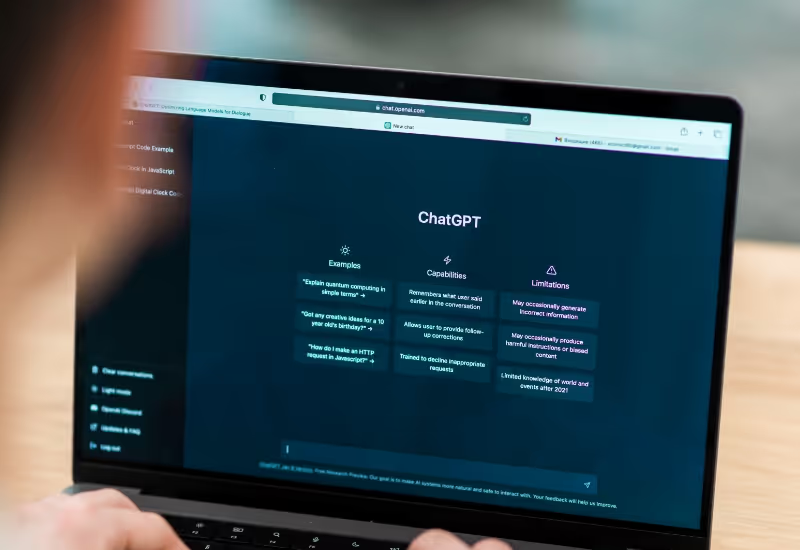
AI tools like ChatGPT, Microsoft Copilot, and Perplexity are being used extensively in the public sector. Sometimes it's planned, but often it happens quietly, out of sight of IT and security. One thing is certain: this technology is here to stay.
That brings opportunities for innovation and productivity, but also a growing risk of data breaches, legal errors, and uncontrolled record-keeping.
For CIOs, now is the time to take the lead. Not by blocking everything, but by setting smart frameworks, getting compliance in order, and facilitating use within safe boundaries.
Also read the blog: Build your own AI colleagues
Using AI without a plan? Here are the risks
More and more employees are using generative AI in their work. Sometimes for brainstorming or summaries, but also for policy memos or draft advice.
Without clear guidelines and technical controls, this creates immediate risks:
- Data is fed into AI tools without any oversight of what happens to it.
- Output may fall under the Public Records Act or the Open Government Act (Woo) without anyone realizing it.
- Decision-making becomes harder to justify or reconstruct.
- Security and compliance come under pressure, especially as shadow IT grows.
In government organizations, this is far from a theoretical problem. You are bound by legislation, transparency requirements, and public scrutiny.
AI output is information, so it falls under your governance.
Using AI doesn't just impact technology; it affects your entire information management strategy.
Output from Copilot or ChatGPT can be archival, for instance when it’s part of decision-making, policy development, or advisory processes. This means it—intentionally or not—falls under the Public Records Act and the Open Government Act.
The question isn't whether you need to set things up, but how quickly you can do it.
Microsoft Purview gives you control—if you set it up right.
Many CIOs already have Microsoft 365 (E5) but aren't yet tapping into its full potential.
With Microsoft Purview, you can also incorporate AI interactions, like prompts and generated responses, into your information management. Think of:
- Retention policies that apply to AI output
- Logging, eDiscovery, and classification
- Restricted access to sensitive AI results
But be careful: this only works if it’s set up correctly from both a legal and technical standpoint. It requires making decisions about retention periods, accessibility, and archival value.
External tools like ChatGPT or Perplexity fall outside this scope. If you want to get a handle on those, you’ll need extra measures, like API integrations or tighter policies.
From preventing incidents to building structure
CIOs who take charge now prevent AI from becoming a major headache later.
By linking clear policies with technical controls, you can give employees the freedom to work with AI without losing control. You’ll prevent incidents, stay on top of things, and remain compliant with laws and regulations.
And just as importantly, you’re building a foundation for the safe, scalable deployment of AI in the future.
Ready to take charge? Start with the basics.
A manageable AI practice starts with setting up Microsoft Purview the right way. Read all about how to do that in this article: Data retention and compliance don't have to be a headache
Curious about where your organization stands? Get in touch with us for a no-obligation exploratory chat.


Frequently asked questions








Fancy a chat?
Do you have a data, cloud or IT transformation challenge? We are happy to think along with you. Feel free to contact us.